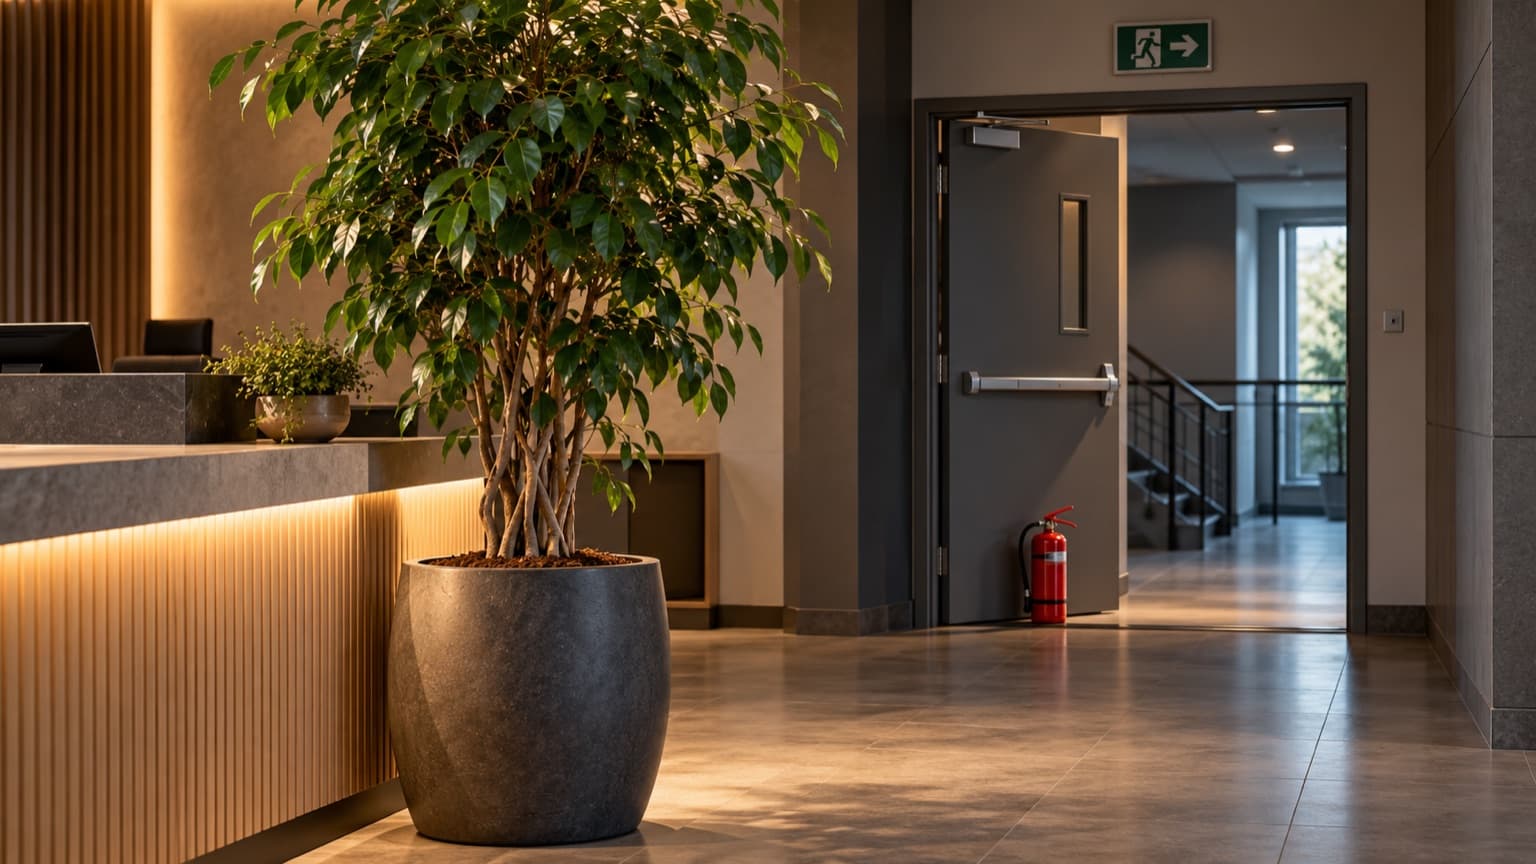
We accept cyber risk the way we pick the plant in reception
On the night of 11 to 12 October 2026, attackers forced the defrosting of refrigerated units in around 700 French supermarkets, through refrigeration controllers reachable from the internet, many of which had not been updated in years. A flaw in those boxes had been reported to Danfoss in February 2023, and the remedy published three months later fitted on one line: restrict network access. A cyber risk is a business risk, and we accept it roughly the way we pick the plant in reception.
On Monday 12 October 2026, CERT-FR, the government incident response centre attached to ANSSI, published an alert on numerous compromises of Danfoss refrigeration controllers, extended the next day to the xweb controllers from Copeland and Dixell. On 13 October, Roland Lescure, the economy minister, told the National Assembly that around 700 supermarkets out of 10,000 had been affected. The Paris public prosecutor handed the investigation to the anti-cybercrime office, tasked with establishing the link between the attack and the damage reported by stores, spoiled food and fires starting. Danfoss replied that the majority of the affected units were older products with no security updates, and that it had long recommended its customers replace them. Its own technical note of October 2025 already described attacks carried out in 2022 against those models, in Russia and in Israel.
None of this was unforeseeable. On 28 February 2023, the firm Synacktiv reported to Danfoss an authentication bypass on those end-of-life boxes, spotted during an audit of a retail chain. The manufacturer replied that only end-of-life products were concerned, and the remedy made public in May 2023 fitted on one line: restrict network access. On the day of the attack, Baptiste Robert, who runs Predicta Lab, still counted 2,752 Danfoss systems exposed online, 1,590 of them in France. According to Synacktiv, that exposure resulted from a configuration the chains had chosen « for convenience ».
The investigation will say how the attackers got in. The question that occupies me arises earlier, and it applies to each of those stores as it does to most of the companies I work with. Somebody accepted that risk, through a signature, through a deferred budget or through silence.
A cyber risk is a business risk, accepted like a furnishing detail
A cyber risk is a business risk, and I see no nuance to add. An attack stops a production line, empties a shelf, delays invoicing, loses a contract or triggers proceedings. It is measured in revenue, in days of downtime, in departed customers and in director liability, exactly like a fire, a fraud or the failure of a major supplier.
The problem starts the moment that risk is accepted. In the committees I sit on and in the registers I review during audits, the acceptance of a cyber risk rarely has the shape of a management decision. It fits on a line in a spreadsheet, in a « decision » column filled with « accepted », sometimes in an email from an IT manager approving it to keep things moving. There is neither an amount nor a review date, and often no name. The decision is taken with the seriousness you bring to choosing the plant in reception: somebody deals with it, nobody mentions it again, and it stays in place for years because nobody thinks to question it.
The image says something precise. Choosing the plant is reversible, has no consequence for anyone, and is gladly delegated to the first person with an opinion. An accepted cyber risk can concern millions of euros, the continuity of the business or the health of people who asked for none of it, and it goes through the same decision circuit.
Why do we accept in cyber what we would refuse for a building?
The exercise I propose at every conference consists of managing a building's risks the way cyber risks are managed, with the same formulas and the same registers.
There are no extinguishers on the ground floor? Never mind, the budget is not there, we will look at it in 2027. Fire doors are missing between the third and seventh floors, with the risk that occupants burn to death in a fire? Risk accepted, documented and signed, since legal and management have approved losses up to 10 million euros, victims included. The gap on emergency exits is identified, it appears in the action plan, subject to budget arbitration. As for ventilation, it is not an immediate business concern, we will look at it the day somebody faints.
Nobody would sign those lines for a building. They nonetheless describe, almost word for word, decisions I watch being taken about information systems. An administration access without multifactor authentication is accepted until the next migration, backups never restored are accepted for lack of time, a device abandoned by its manufacturer is accepted because it « still works ». The structure of the decision is identical, and the possible consequence weighs just as heavily at the scale of the company.
The day the fire starts, what follows is familiar. Management calls a general meeting, blames « legacy », promises lessons learned, then the next committee reopens the register and moves on to the following acceptance. In cyber, that is the story of our lives.
In a building, the law took the decision away from the business
The line about fire doors does not get signed, because the law leaves no room for that signature. A French supermarket is a type M public-access establishment, subject to the fire and panic safety regulation approved by the order of 25 June 1980 and supplemented, for shops, by the order of 22 December 1981. It admits the public only after the safety commission has visited, and the commission returns at regular intervals according to its category. The labour code requires at least one six-litre water-spray portable extinguisher per 200 square metres, in Article R4227-29, and the safety regulation requires it to be checked annually.
When the commission issues an unfavourable opinion, Article L143-3 of the construction and housing code allows the mayor or the prefect to order the establishment closed until it is brought into compliance. In 2024, the mayor of Fresnes, in Val-de-Marne, closed a Casino hypermarket after visits that had found more than a dozen irregularities. The supermarket does not choose its level of fire safety. It applies it, funds it and has it inspected.
A director who wrote down in black and white that they accept the absence of fire doors would above all be manufacturing evidence. Article 223-1 of the penal code punishes with one year of imprisonment and a 15,000 euro fine the act of exposing others to an immediate risk of death or of injuries liable to cause mutilation or permanent disability, through the manifestly deliberate violation of a specific safety obligation imposed by law or regulation. It would be hard to find better proof of deliberateness than a dated and signed acceptance.
Building law therefore sets a floor below which nobody has the power to accept anything. The trade-off exists, and it begins above that floor: choosing between two compliant smoke extraction systems, postponing a refurbishment, forgoing a comfort feature. The occupants sign nothing, and it is precisely for that reason that the rule decides in their place what is not negotiable.
Why does cyber risk have no safety commission?
Nothing comparable exists for most of a company's cyber risks. No commission comes to check, before opening, that remote access requires a second factor, and no mayor closes a site because its backups have never been restored. The supermarket keeps a fire safety register, inspected at every visit, and the box that runs its cold chain appears in no equivalent document.
NIS2 is starting to set a floor. Its Article 21 lists the measures expected of the entities in scope, and its Article 20 gives their approval to the management bodies, who may be held liable for failures. In food, it covers wholesale distribution and industrial production: a supermarket selling at retail does not fall in scope on that basis alone, even though the group it belongs to may fall in scope through its warehouses or distribution centres. The French transposition, for its part, passed 17 October 2026 with two years of delay and still no vote, and I recently wrote what I think of those who wait for the law to act: Parliament has never been your CISO. Even in force, the directive will remain the bare minimum.
Cyber above all combines everything that makes a casual acceptance easy. The risk cannot be seen and does not smell of smoke. Its consequences arrive months after the decision, rarely on the desk of the person who took it. It is presented to the committee in a tooling vocabulary, a criticality score, a gap against a framework control, that nobody around the table knows how to convert into losses. And it comes back every year in the same budget discussion, which turns each postponement into a habit. The night of 11 October, for that matter, erased the boundary between IT risk and physical risk. According to Les Mousquetaires, the affected refrigerators in Intermarché stores were taken to 50 °C for six hours, and the Paris public prosecutor is investigating fires starting. The fire analogy I develop on stage stopped being an analogy that night.
Accepting a risk is a decision, with a signatory, a criterion and a deadline
Accepting a risk is a legitimate treatment option, and the standards provide for it. ISO 31000, the reference standard in risk management, allows a risk to be retained provided it results from an informed decision. ISO/IEC 27001 draws precise requirements from that. Acceptance criteria must be defined before any assessment (clause 6.1.2 a). Each risk must have an owner, meaning a person with the authority and responsibility to manage it (clause 6.1.2 c). It is those owners who approve the treatment plan and accept the residual risks (clause 6.1.3 f). In an audit, I therefore always ask the same three questions: who signed, on the basis of what criterion, and until when.
A defensible acceptance rests on a few elements any committee can demand. The scenario is expressed in consequences for the business, with a quantified order of magnitude, and the technical score stays in an annex for those who have a use for it. The signatory has authority proportionate to the impact: in a company whose executive management has set risk appetite at 500,000 euros, a 10 million scenario is not accepted at the level of an IT manager. The decision sets out the compensating measures that make it tolerable, enhanced monitoring, restricted access, network isolation. Finally it carries an expiry date, beyond which it lapses and returns automatically to the committee.
« We will see in 2027 » meets none of those conditions. It is a treatment plan with a date attached, which is fine as long as the date is met. The day it slips without anyone going back to the committee, the risk becomes accepted by default, with no signatory and no criterion, and that is the form of acceptance I come across most often. Registers accommodate it very well. The line stays « in progress », the action plan continues to exist, written like a prayer, and nobody can say at what moment the company decided to live with it.
There are risks no signature makes acceptable
The parallel with buildings goes further than the image. Some cyber risks look exactly like a missing fire door, and no acceptance procedure, however perfectly documented, should be able to cover them.
A risk whose impact exceeds the authority of everyone in the room is one of them. If the possible consequence is the lasting shutdown of the business, the signature of an operational committee is worth nothing, and the subject goes to the board or it does not get signed.
Risks borne by others follow the same logic. The occupants of a building sign nothing, no more than the customers whose data is exposed, the patients of a hospital or the consumers who buy a fresh product. A company can decide to risk its own money, and it has no legitimacy to accept alone a risk that falls on third parties.
That leaves the structural defect whose fix is known and cheap. A device abandoned by its manufacturer and reachable from the internet will never receive another patch, so the acceptance covering it no longer has any possible deadline and becomes permanent. CERT-FR warns, for that matter, that a simple reset is not enough: a device left online with no patch remains destined for a « very high probability of compromise » and will be compromised again. Disconnecting it costs almost nothing, and it is the first measure in its alert, the one Vincent Strubel, director general of ANSSI, called urgent. An administration access with no second factor or a critical backup never restored belong to the same family. You do not work around a structural defect with a spreadsheet, and the risk simply waits for the right Monday morning.
Between not blocking the business and never blocking anything, there are two worlds
I am the first to say that security must not block the business. It exists to serve it, and the CISO who expects the company to put itself at the service of their roadmap, a posture I often find in coaching, loses their arbitrations for good reasons. Accepting a risk is part of normal work: launching a product with a known residual risk, keeping an old application for six months behind compensating measures, opening a market before a compliance programme is finished. A security function that refuses everything pushes teams towards workarounds it no longer sees, and the risk grows out of its sight.
In the first world, the company takes risks knowingly. It knows what it is accepting, how much it could cost, who signed and when the decision will be reviewed, and it rules out without discussion the short list of what is never accepted. In the second, nothing is ever refused. The register records the accumulation, each postponement becomes a silent acceptance, and the documentation ends up serving mainly to prove that you knew.
The CERT-FR alert draws the boundary between the two precisely. It asks for the direct exposure of the controllers to be removed, then for refrigeration engineers' access to be restored through a VPN or a protected network, and advises checking the insurance contract before cutting the data feed to the provider. Remote maintenance has an economic and sometimes contractual reason to exist, and nobody is proposing to give it up. Leaving an administration interface open on the internet, three and a half years after the remedy was published, belonged to the second world.
I have stopped working with several organisations, under NIS2 as under DORA, because they refused the legal minimum. They all lived in the second world.
What would make a risk acceptance defensible
A management team that wants to be done with the reception plant needs neither a new framework nor a law. Before the 2027 budgets close, its executive committee can adopt written acceptance criteria, expressed in euros, in days of downtime and in impact on third parties, with explicit authority levels: what an operational manager can accept, what goes up to the executive committee, what goes up to the board.
Each acceptance should then carry a name, a quantified scenario, its compensating measures and an expiry date of twelve months at most. An expired acceptance returns automatically to the committee, and no tacit renewal is allowed.
The most useful piece of work is the inventory of risks accepted by default, those action plans whose deadline has passed and those devices nobody updates any more. For each one, management demands an explicit decision in the first quarter of 2027: treated, or accepted by somebody who signs.
It then remains to write its own fire code, a short list of what is never accepted, whatever the budget. An end-of-life device reachable from the internet, a remote or administration access with no multifactor authentication, a critical backup never restored. Three lines are enough to start, and they fit on the same page as the plant order.
In a building, the line « fire doors missing from the 3rd to the 7th floor, risk accepted » would read in court as the admission of a deliberate violation. In a cyber risk committee, the same line is called a management decision, and it is taken with the care you bring to choosing the plant in reception.
Further reading
- Parliament has never been your CISO
- The only backup that counts is the one you have already restored
- ReCyF, backdoors and USB sticks: France in cybersecurity, between clarity and anachronism
- Free: the fine is being argued at the Conseil d'État, the phishing carries on
- Cybersecurity must not become an election issue
- PECB Insights, « What the 50 Missions I Oversaw Taught Me About Europe's Biggest Cyber Bet », The Expert column
- etrecyber.fr: the practical steps, without the jargon
Sources
- CERT-FR, Incident de sécurité ciblant les contrôleurs à distance des installations de réfrigération, alert CERTFR-2026-ALE-012 of 12 October 2026, updated 13 and 16 October 2026.
- LSA, Cyberattaque des frigos : le récit étape par étape du hacking de 700 magasins, October 2026, for Roland Lescure's statement to the National Assembly on 13 October 2026.
- AFP, dispatch of 12 October 2026, for the Paris public prosecutor's statement (referral to the anti-cybercrime office, spoiled food and fires starting); Reuters, 12 October 2026, for the statement by Les Mousquetaires (50 °C for six hours) and that of Danfoss; BleepingComputer, Cyberattack shuts down refrigerators at French supermarkets, 12 October 2026, for the Predicta Lab count.
- Public Sénat, Cyberattaque contre des frigos connectés de supermarchés : « Des systèmes de réfrigération exposés sur Internet », alertent des experts en cybersécurité, 13 October 2026, for the statements by Kevin Tellier (Synacktiv), Vincent Strubel (ANSSI) and Danfoss.
- Synacktiv, Authentication bypass in Danfoss System-Managers model SM800 & SC255/SC355, advisory published 22 May 2023 and updated 31 October 2023.
- L'Usine digitale, Frigos de supermarchés sabotés : des contrôleurs Danfoss obsolètes, des failles documentées et des responsabilités à éclaircir, and InformatiqueNews, October 2026, for the Danfoss technical note of October 2025 (2022 attacks in Russia and Israel, AK-SM 800 end of life in May 2021).
- ISO 31000:2018, Risk management, guidelines, clause 6.5.2; ISO/IEC 27001:2022, clauses 6.1.2, 6.1.3 and 8.2.
- Directive (EU) 2022/2555 of 14 December 2022, known as NIS2, Articles 20 and 21 and Annex II.
- Order of 25 June 1980 approving the general provisions of the fire and panic safety regulation in public-access establishments; order of 22 December 1981 on type M establishments.
- French construction and housing code, Article L143-3; labour code, Article R4227-29; penal code, Article 223-1.
- Commune of Fresnes, order no. AR-2024-102 ordering the closure of the public-access establishment « Hypermarché Casino », 2024.
Frequently asked questions
What is an accepted risk in cybersecurity?
It is a risk the organisation decides to keep as it is after assessing it, without seeking to reduce it further. ISO 31000 and ISO/IEC 27001 allow that option provided it rests on an informed decision, taken by the risk owner according to criteria set in advance. A risk set aside for lack of budget, with no formal decision, is simply endured.
Who can accept a cyber risk in a company?
The risk owner, in the sense of ISO/IEC 27001, meaning the person with the authority and responsibility to manage it. Their level must be proportionate to the possible impact: the heavier the consequence for the business, the higher the signature must come from. For entities subject to NIS2, Article 20 gives approval of risk management measures to the management bodies.
How long does a risk acceptance remain valid?
No standard sets a single duration, but ISO/IEC 27001 requires risks to be reassessed at planned intervals and upon any significant change (clause 8.2). A validity of twelve months at most, with automatic return to the committee, is a defensible practice. An acceptance with no expiry date always ends up covering a situation that bears no resemblance to the one that was assessed.
Does security not risk blocking the business?
It can, and a security function that says no to everything pushes teams to work around its rules. Risk acceptance exists precisely to let the business move forward with a known and quantified risk. What causes problems is acceptance with no criterion, no authorised signatory and no deadline, along with the handful of risks, like an end-of-life device reachable from the internet, that no signature should cover.
Why compare cyber risk to fire risk?
Both threaten business continuity and, increasingly, the safety of people outside the company. The fire risk of a public-access establishment is nonetheless governed by regulation, checked by a commission and punishable by administrative closure. Cyber risk remains, for most companies, left to their management's judgement, which makes the quality of their acceptance decisions all the more decisive.
What happened with the supermarket refrigeration controllers?
On the night of 11 to 12 October 2026, attackers remotely forced the defrosting of refrigerated units in around 700 French supermarkets, according to the economy minister. CERT-FR reports numerous compromises of Danfoss AK-SM and AK-SC controllers as well as Copeland and Dixell xweb, and Danfoss states that the majority of its affected units were older models with no security update. The Paris public prosecutor has opened an investigation, no claim of responsibility has been made public and the means of intrusion was not established at the date of this article.
Are supermarkets covered by NIS2?
Not as retail shops. In the food sector, Annex II of the directive covers companies engaged in wholesale distribution and industrial production or processing. A retail group may fall in scope through its warehouses, its distribution centres or its industrial activities, but the store itself remains master of its cyber trade-offs, and therefore of its risk acceptances.
The author
Christophe MazzolaI write about cybersecurity as it's actually lived: governance, the human factor, and everything audit reports don't dare tell the board. Author of « Être en cybersécurité ».
Être en cybersécurité
A cyber roadmap in plain language, for everyone, not just the experts.