The threat that has never claimed a victim, and comes back on the evening news every summer
On 6 August, BFMTV explained why you should beware of public USB ports. The technique exists, it works, it is even formidable in the hands of a targeted attacker. On an airport charging station, in fifteen years, nobody has ever documented a single case.
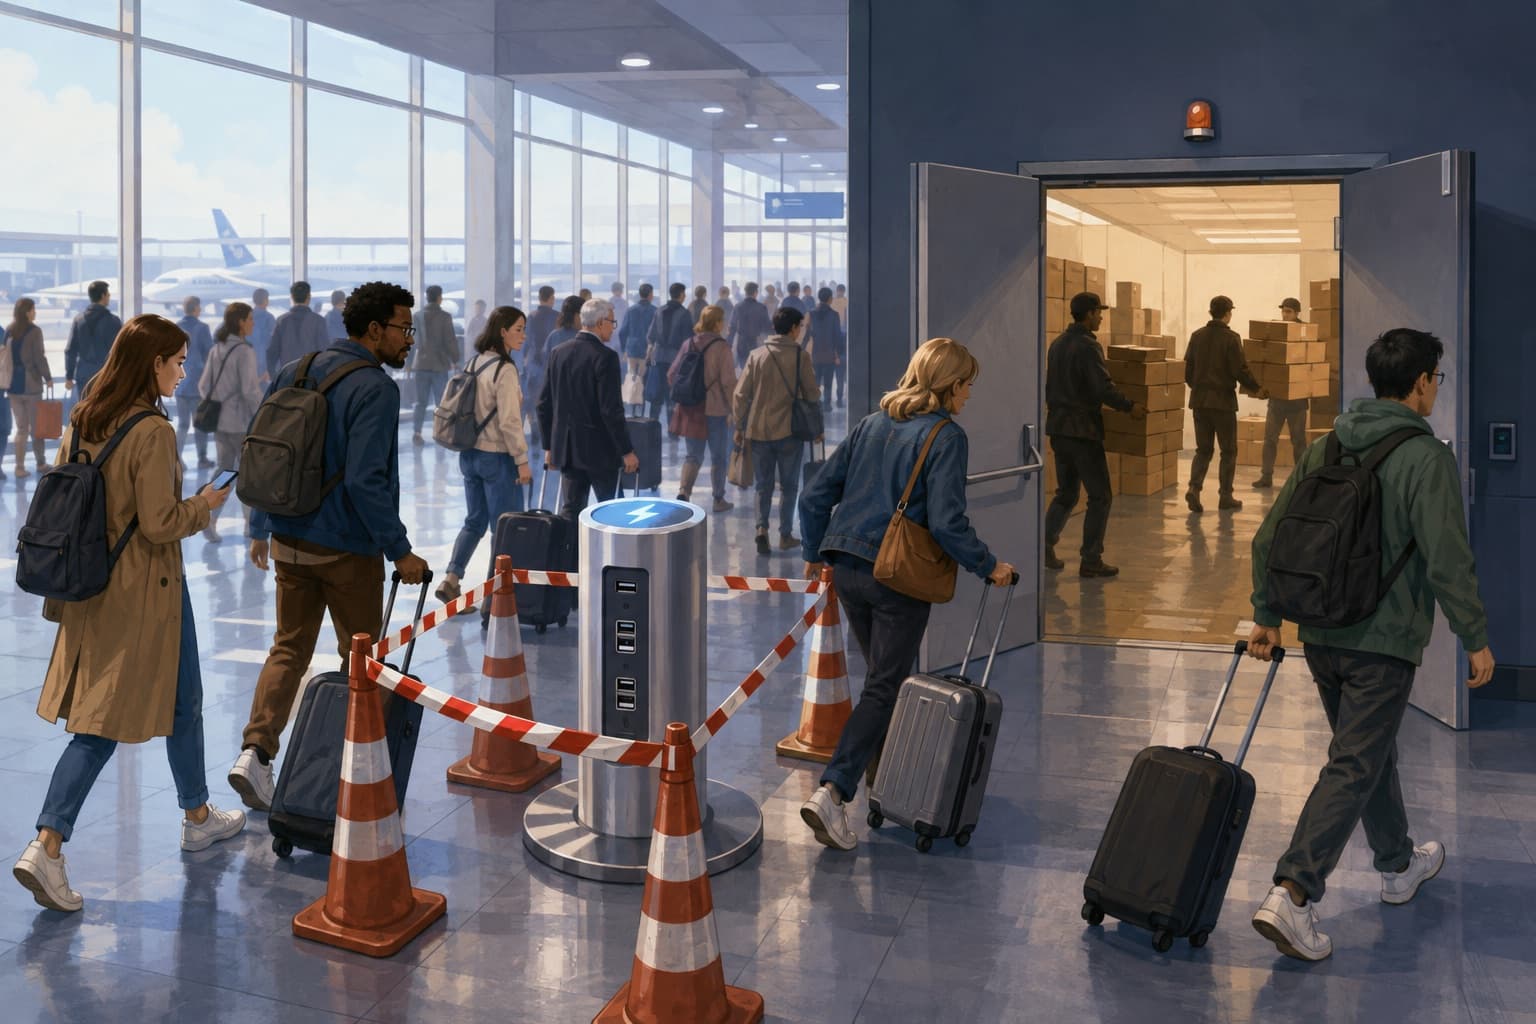
In April 2023, the FBI's Denver field office posted a tweet advising people to avoid public charging stations. A Slate journalist called to ask which incident had prompted the warning. The FBI's answer: none. It was a routine reminder, lifted from an FCC advice page dating from 2019.
Within a week, CNBC, the Washington Post, CNN and Good Morning America treated the subject as an alert. The FCC, swamped with calls about a file it had not reopened, then updated its own page to keep up. That update became a fresh source, which fed the next wave.
The TSA picked it up again in 2025. The French gendarmerie recommends the USB data blocker. A power bank manufacturer published an explainer on the subject in July 2026, which will surprise nobody. BFMTV closed the loop on 6 August.
At no point in this chain did anyone produce a victim. What circulates is not the information, it is its shape.
What juice jacking really does, and where it does not
The USB attack exists and it works. An O.MG-type cable, sold openly, contains an implant that grants remote full access to the machine it is plugged into, and nothing distinguishes it visually from an ordinary cable. Malicious USB devices are a documented vector in targeted operations, including campaigns where rigged drives were mailed to named victims. An attacker who leaves a modified cable in a meeting room, hands one out as swag at a trade show, or swaps the one in the charger of a hotel room booked in an executive's name is doing something entirely real, and sometimes very effective.
That is not what the reports are about. They are about the USB socket in the airport concourse, the train, the shopping centre. About an anonymous attacker rigging a fixed piece of equipment to reach a victim they have not chosen.
On that precise scenario, the picture is different. The FCC, source of the advice sheet everyone recycles, has acknowledged knowing of no confirmed case. Apple states it is unaware of any such attack in the wild on its devices. The term was coined in 2011, when researchers set up a rigged charging station at DEF CON to demonstrate the risk. Fifteen years later, the demonstration is still the only item in the file.
Juice jacking in its public-charging-point version is therefore a real technique transposed into a context where it does not occur. It is the gap between the two that ought to interest a newsroom.
How a 2019 advice sheet ends up on the 2026 evening news
An agency republishes an old warning, with nothing new. Media coverage treats the republication as an event. The volume of questions generated by that coverage pushes the originating agency to refresh its page, which produces a source dated today. That source feeds the next wave, six months or a year later, and the cycle restarts without a single new fact having entered the system at any point.
This is neither a lie nor a manipulation. It is a feedback loop in which every actor behaves reasonably at their own scale. The journalist sees a warning from a federal agency and covers it. The agency sees public demand and updates its documentation. The expert consulted confirms that the technique exists, which is true. Nobody has any reason to check the number of victims, because nobody claimed there were any.
The missing information is never denied. It is simply never requested.
Why a public charging point is a very poor investment for an attacker
Rigging a charging point requires physical access to fixed equipment, generally installed in an area under video surveillance, with a non-zero risk of arrest. The return on that operation is one unchosen victim, whose device will in any case demand explicit authorisation before allowing any data transfer, and whose value is unknown before compromise. It has to be done again for every target.
Against that, a phishing link costs nothing, reaches ten thousand people in a minute, carries no physical risk and allows the population to be selected. An unpatched vulnerability on exposed equipment can be scanned for automatically at internet scale and monetised across thousands of organisations in parallel.
Attackers are rational actors under resource constraints. Mass juice jacking never took off for the same reason handbag theft was never industrialised: the effort-to-return ratio is poor, and there is better elsewhere.
What actually compromises organisations in 2026
Verizon's 2026 Data Breach Investigations Report analysed more than twenty-two thousand confirmed breaches across one hundred and forty-five countries. For the first time in nineteen editions, vulnerability exploitation becomes the leading initial access vector, at 31%, against 20% the year before. Phishing sits at 16%, credential abuse at 13%, or 16% on a constant methodology. The human element appears in 62% of breaches and that figure has not moved for three editions, which ought to prompt questions of the awareness industry before questions of users.
The figure that should be leading the evening news is elsewhere. In 2025, only 26% of vulnerabilities known to be actively exploited were patched, against 38% the previous year. In other words, three doors out of four that we know for certain attackers are walking through right now were left open. The exposure window is not closing, it is widening. Over the same period, breaches involving a third party rose 60% in a year to reach 48% of cases.
Your security posture therefore no longer depends only on your decisions, but on the patches applied by your payroll provider, your line-of-business vendor and your host.
In France, no major breach came through a USB port
On 15 April 2026, the national agency for secure documents, the one that issues passports, identity cards, driving licences and vehicle registrations, detected an intrusion on its user portal. Five days later the interior ministry confirmed access to the personal data of 11.7 million accounts, with the attacker claiming 18 to 19 million on forums. The flaw exploited was an IDOR: changing an identifier in a request was enough to view another user's file. It is the vulnerability you learn to spot in the first week of training. The alleged author is fifteen and called it stupid himself. The political response was a state cyber plan worth 200 million euros.
Two years earlier, in March 2024, attackers had hijacked the credentials of Cap Emploi advisers to reach a France Travail database holding twenty years of registrations. Potentially 43 million people, reduced to 36.8 million after deduplication. The CNIL issued a five million euro fine in January 2026, explicitly citing the inadequacy of the password policy. Viamedis and Almerys, hit five days apart in 2024 by the same method, had exposed 33 million insured people, and Almerys was the subject of a fresh claim in May 2026, larger in volume than the first. Cegedim Santé, publisher of software used by 3,800 doctors, confirmed its intrusion on 26 February 2026, with the health minister citing more than fifteen million people affected.
These are not isolated cases lined up for effect. The CNIL received 6,167 breach notifications in 2025, up 10% year on year. Since January 2026, specialist trackers count more than three hundred compromised services in France and roughly 250 million exposed personal records. In May, Le Monde described French citizens as vulnerable in the face of powerless authorities.
Look for the charging station in that list. Look for the spectacular zero-day, the deepfake, the cinematic SIM swap. What there is instead is corporate accounts without strong authentication and unapplied patches, year after year, in systems that hold the entire population.
The France Travail penalty is instructive for another reason. An administrative authority is penalising a public operator for failings that small businesses have been lectured about for fifteen years. Asking citizens to be careful is legitimate. Doing so at that level of risk concentration without holding the same standard at home is markedly less so.
The mass risk nobody films: the photo of your ID card
There is a category of risk that ticks every box of the massive, everyday, structural problem, and no box of the media narrative.
Sending a high-resolution scan of your identity card to a platform you know nothing about has become an ordinary act. To open a resale account, validate a profile, sign up for a service, millions of people transmit a document every week to companies whose servers they cannot locate, whose retention period they do not know, whose subcontractor processes the image, and whose backups they cannot account for.
A compromised password is changed in thirty seconds. A compromised identity document follows you for ten years and is resold, because it opens lines of credit and passes identity checks elsewhere. In October 2025, roughly 70,000 photos of identity documents collected by Discord leaked, not from Discord but from its customer support subcontractor. The breaking point is almost never the front door, it is the complaints desk.
This transfer of risk happens at population scale, it is irreversible for the victim, and it is the subject of no explainer video. The difference with the USB charging point is not severity. It is that naming the identity document risk means naming identifiable responsible parties, some of whom are advertisers.
Is public Wi-Fi still dangerous in 2026?
On the train, at the hotel, at DEF CON, in a café: connect. The open network is no longer the problem. That fear is a relic of an era when traffic mostly travelled in the clear, when passive interception gave access to entire sessions, when a rogue access point replayed your cookies effortlessly. Transport encryption has become the overwhelming norm, HSTS prevents downgrade on the sites that matter, certificate transparency makes the issuance of a fraudulent certificate detectable, and modern systems isolate applications from one another. On an up-to-date machine, an attacker positioned on the network sees essentially metadata.
The residual risk exists but it has changed in nature. It is no longer interception, it is the captive portal imitating a login page to harvest credentials, which is phishing in a different setting. Or it is the exploitation of an unmaintained system, in which case the network is only one path among others and the problem lies elsewhere.
The consumer VPN sold as network protection is a cure for a largely cured disease. It has real uses, circumventing geographic restrictions and withholding your history from your internet provider. It does not fix an unpatched system, and it moves your trust from the café operator to a commercial operator you know even less well.
The last place where you can still act
Take the 250 million records exposed in France since January. Ask yourself, for each one, what the person concerned could have done.
They did not choose to create an account on the secure documents portal, the state removed the physical counter. They did not choose their doctor's software. They did not choose that their health insurer works through that claims administrator. They cannot change their date of birth after the breach, nor their social security number, nor their address. A unique password and strong authentication, which are excellent advice in general, would have changed absolutely nothing about an IDOR on a public agency portal.
For the overwhelming majority of what leaked in France this year, the victim's behaviour was not a variable. That is a rupture, and it goes unsaid. The whole public culture of cybersecurity was built on a model where risk plays out at the moment of the individual act: the click, the password, the plug. That model correctly described the 2000s. It describes nothing today, because risk has moved to the architecture of the systems that hold your data and to the decisions of those who operate them, which is to say to a place where you have no leverage.
Individual advice has outlived individual agency. And it has survived precisely because it is the last register in which anyone can still be addressed. A report on the USB charging point gives the viewer a role, a decision to make, a habit to change on getting up from the sofa. An accurate report on the concentration of public data teaches them that they are exposed, that they can do nothing about it, and that those responsible are beyond their reach. The first format runs every summer. The second does not exist, because it has no ending.
That is what the 6 August segment is really about. Not a misjudgement of an attack vector. The artificial maintenance of a regime in which the citizen would still be the agent of their own security, at a moment when they no longer are.
That maintenance has a political price. It produces a population, and above all leaders, who model cybersecurity as a matter of personal hygiene, at the exact moment it has become a question of architecture and concentration. It is what allows a trivial flaw on the identity documents portal to be answered with a 200 million euro plan and vigilance advice to users, rather than with a debate about having built a single point of failure holding the identity of eleven million people.
Why newsrooms prefer the exotic threat
Fear draws an audience, and that answer is too short. An exotic threat has the immense narrative advantage of being external. The rigged USB port, the voice deepfake, the novelistic SIM swap are stories in which the viewer is subjected to an ingenuity beyond them. Nobody is at fault, no practice is called into question, and the piece closes neatly on free advice that commits to nothing. To say instead that most breaches come through unapplied patches and accounts without strong authentication is to name identifiable responsible parties, some of them institutions, some of them advertisers, and some of them the viewer.
The cybersecurity industry holds its share of the market. A vendor has infinitely more interest in commenting on a novel threat than in repeating that patch management and strong authentication settle most of the problem, because the first conversation sells a product category and the second sells operational discipline, which cannot be invoiced in licences. The journalist needs an available expert, the expert needs a marketable subject, and the deal closes without either having to lie.
What a false priority actually costs
Attention to security is a finite resource, and it is countable: one awareness module, one board slot, one internal campaign.
Every unit spent on a scenario never observed is a unit taken from the decisions that matter. An organisation that trains its teams to beware of charging stations while three quarters of its actively exploited vulnerabilities go unpatched has not done a little security. It has produced an indicator, and that indicator will rise. This is the green dashboard: the metric improves, the risk does not move, and nobody asks questions any more because the colour is good.
The real cost is paid at the moment of decision. A leader who has internalised that cybersecurity is about individual gestures and travel gadgets will rule against a patch management budget, because nothing they have read has made them understand that this is where the game is played.
What remains open
The easy correction fits into a question to be asked systematically, in a newsroom as on a board, in the face of any alert: how many documented victims, and over what period. It costs nothing and it eliminates most of the noise.
The hard correction is to accept that the boring subject is the main subject, and will remain so. Patch management, strong authentication, supplier control and account revocation will never make a twenty-minute segment. They only produce the overwhelming majority of breaches when they are absent.
Then there is the question neither correction settles. We will go on telling people what to do because it is the only thing we still know how to tell them, and because informing them that their vigilance now counts for nothing against an IDOR in a public agency is not a message an institution can carry. Juice jacking is therefore not a failure of cybersecurity reporting. It is the last subject in which you can still be assigned a role, and that is why it will be back next summer.
Sources
- Absence of confirmed cases and origin of the warning: Slate investigation, April 2023, including responses from FBI Denver and the FCC.
- The TSA repeating the warning in 2025 and the absence of any documented real incident since: Malwarebytes, June 2025.
- History of the technique since DEF CON 2011, Trustjacking research and the O.MG cable: ESET, juice jacking dossier, 2026.
- Apple's position on the absence of observed attacks in the wild: quoted by Ars Technica, 2023.
- Initial access vectors, human element, remediation of exploited vulnerabilities and third-party breaches: Verizon Data Breach Investigations Report 2026, published 19 May 2026.
- France Travail breach and the five million euro penalty: CNIL decision and communication, January 2026; deduplication figures provided by France Travail to AFP.
- Viamedis and Almerys breach, more than 33 million people: CNIL communication, February 2024. Fresh Almerys claim, May 2026.
- ANTS / France Titres intrusion of 15 April 2026, ministerial confirmation on 20 April, IDOR flaw, 11.7 million accounts and a claim of 18 to 19 million: interior ministry statement, Generation-NT, FrenchBreaches, April 2026.
- Cegedim Santé breach, public confirmation on 26 February 2026, more than fifteen million people affected according to the health minister.
- 2025 and 2026 volumes: 6,167 breach notifications received by the CNIL in 2025, up 10%; more than three hundred compromised services and roughly 250 million records recorded in France since January 2026 by specialist trackers, as of June 2026. Le Monde coverage of 18 May 2026.
- Leak of identity documents collected by Discord through a subcontractor: Discord statements, October 2025.
Frequently asked questions
Is juice jacking real?
Yes, as a technique. A rigged USB cable or device can compromise a machine, and implants of this kind are sold commercially. What has never been documented is the exploitation of this vector through a compromised public charging station.
How many juice jacking victims have been recorded?
None publicly, on public charging points and modern devices. The US FCC has acknowledged knowing of no confirmed case, and Apple states it has observed no such attack in the wild.
Should I still use a USB data blocker?
The accessory is cheap and harmless, so there is nothing against it. It simply should not be mistaken for a meaningful security measure. For the same amount of attention, enabling automatic updates and strong authentication on sensitive accounts has an incomparably greater effect.
Can I plug my phone into the USB socket on a plane or in a hotel?
Yes. Current mobile systems require explicit confirmation before allowing any data transfer over a USB connection, which neutralises the scenario. The real issue lies elsewhere, on a device that is not up to date.
Is public Wi-Fi dangerous?
Far less so than in 2010. Transport encryption, HSTS and certificate transparency have removed most of the interception risk. What remains is a phishing risk through a fake captive portal, and the exploitation of an unmaintained system.
What is the most common attack vector today?
According to Verizon's 2026 DBIR, the exploitation of unpatched vulnerabilities, present in 31% of breaches, ahead of phishing at 16% and credential abuse at 13%.
What can I do about a breach like the one at the French identity documents agency?
Nothing beforehand, and that is the heart of the problem. No individual practice prevents the exploitation of a flaw on the portal of a public agency where you were required to create an account. Afterwards, you can reset your passwords, enable strong authentication and treat as suspect any message claiming to come from the organisation concerned, which limits the secondary exploitation of the breach without changing the breach itself.
Which measures actually protect you?
Automatic updates, a password manager with unique credentials, two-factor authentication that does not rely on SMS, and for an organisation, a measured remediation time on actively exploited vulnerabilities together with real control over the access granted to suppliers.
The author
Christophe MazzolaI write about cybersecurity as it's actually lived: governance, the human factor, and everything audit reports don't dare tell the board. Author of « Être en cybersécurité ».
Être en cybersécurité
A cyber roadmap in plain language, for everyone, not just the experts.